DEVELOPER · REMOTE MCP PLUGIN
Zovo Dependency Audit
Audit a dependency list for known vulnerabilities, licenses and outdated versions with OSV.dev and deps.dev records.
Live official dataThe answer comes from OSV.dev vulnerability database and deps.dev at the time you ask. Each result shows the source and the retrieval time in UTC.See all live data plugins
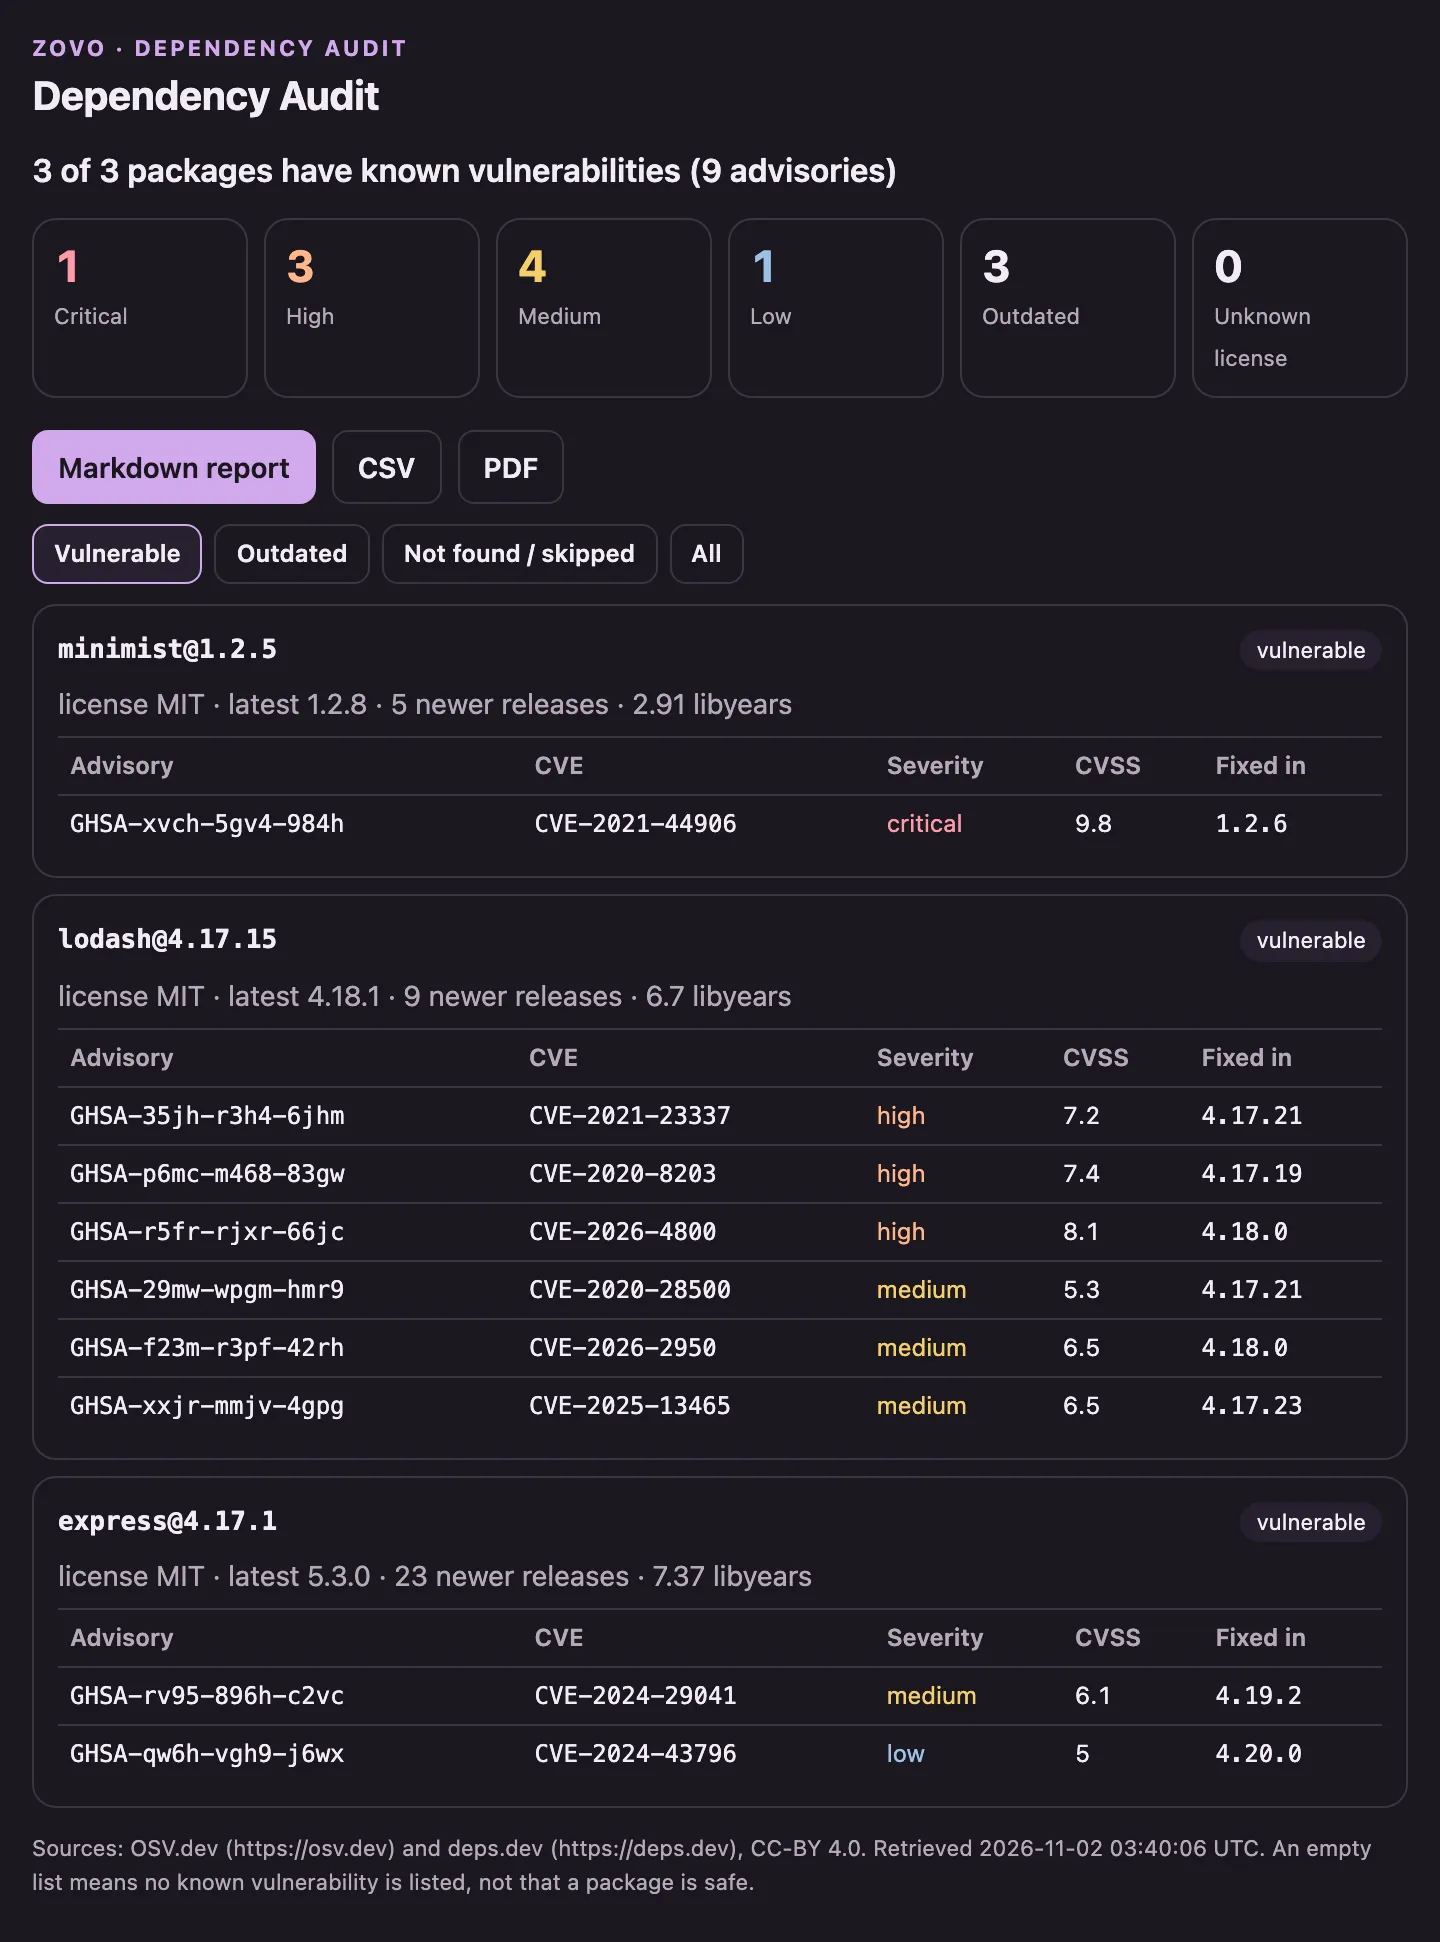
You askAudit these npm packages for vulnerabilities. lodash@4.17.15, minimist@1.2.5, express@4.17.1
RELEASE CHECK · 2 NOV 2026
A release review is not recorded yet.
This server is live and passed its build checks on 2 Nov 2026. An independent release review isn't recorded here yet. Inspect its limits and test a synthetic example before relying on it.
See the fleet snapshot and its limits ↗Custom connections require support in your AI app, plan, and workspace. Follow the host guide before you use the prompt.
A TASK TO TRY
Give the plugin a clear task.
Audit these npm packages for vulnerabilities. lodash@4.17.15, minimist@1.2.5, express@4.17.1
BEFORE YOU CONNECT
Check the limits.
Anonymous server discovery is checked. A current installation and widget test in both hosts is not recorded for this release.
- It reads direct dependencies only. It does not resolve the transitive tree or read lockfiles.
- An empty list means OSV.dev lists no known vulnerability for that version, not that the package is safe.
- npm, PyPI, Go, crates.io and Maven, up to 300 packages per audit.
- License data is not legal advice.
WHAT THE SERVER EXPOSES
2 functions to request.
Names and descriptions below come from live MCP discovery. They describe the server; they are not a test of every function in ChatGPT or Claude.
Audit dependencies
audit_dependenciesUse this when the user pastes a dependency manifest (package.json, requirements.txt, go.mod, Cargo.toml, pom.xml, or one name@version per line) and wants known vulnerabilities with fixed-in versions, licenses and outdated packages, as a Markdown report for a pull request plus CSV and PDF. Reads live OSV.dev and deps.dev records. Up to 300 packages per call; ranges are checked at their stated minimum version. Does not resolve transitive dependencies, read lockfiles, scan source code or fix code. Do not use for container images or operating system packages.
Check one package
check_packageUse this when the user asks whether one specific package version has known vulnerabilities, which version fixes them, its license, or how outdated it is (for example lodash 4.17.15 on npm). Reads live OSV.dev and deps.dev records and returns Markdown, CSV and PDF reports. Needs one specific version, not a range. Does not check transitive dependencies or scan code.
Connect. Ask. Check.
- Use the setup guide for ChatGPT or Claude. Copy this plugin's endpoint.
- Connect the tool. Paste the sample prompt and supply the inputs it needs.
- Review the result before you rely on it. Check the source tool's limits and privacy terms.
ADAPT THIS TASK TO YOUR WORK
Need a different input or output?
Start a brief from Zovo Dependency Audit. Describe your inputs, the result you need, and the checks that define a useful result. Download it before you share it.
The brief runs in your browser. Custom projects need a separate scope and price agreement.
COLLECTIONS